Case study
Daily Agenda: building a planner the server can't read.
A self-initiated web app I designed and built solo — a personal planner with genuine end-to-end encryption, where every task, recurring routine, and quick-captured note stays private by architecture, not policy.
Product designPrivacy & securityFront-end build5 min read
- SoloDesign → Build → Ship
- 5Real bugs found & fixed
- 0Tasks the server can read
- React + SupabasePlatform
Overview
The short version
Daily Agenda is a personal planner built around one non-negotiable: the server that stores your tasks should never be able to read them. Everything — tasks, recurring routines, quick-captured notes — is encrypted client-side before it ever leaves the browser.
I owned the project end to end: problem framing, information architecture, UI design (built directly in code), full-stack engineering, encryption architecture, and ongoing testing through real daily use.
- Role
- Product Designer · Front-End & Full-Stack Developer
- Team
- Solo project
- Platform
- Web (React + Supabase)
- Timeline
- Ongoing
- Tools
- React, Vite, Supabase, Vercel
- Focus
- Genuine privacy & everyday reliability
The problem
Most planners can read what you write
Most to-do apps ask you to trust a server with your plans, and call it secure because it’s ‘encrypted at rest’ — a guarantee about the company’s compliance checklist, not about what they can actually read. Layered on top of that is a more everyday failure: recurring tasks that duplicate or don’t fully delete, unfinished tasks that vanish instead of carrying over, and day boundaries that quietly flip before actual local midnight. Both problems erode the same thing — trust that the planner will do exactly what it says, every time.
Goals & success metrics
What the app had to do
Clear objectives from day one — framed as verifiable engineering and UX benchmarks rather than growth metrics, since this is a private, personal-use tool with no analytics.
Goals
- Build genuine end-to-end encryption — the server never sees a readable passphrase or task
- Make recurring tasks, carryover, and categorization behave correctly under real daily use
- Keep security from becoming friction that gets in the way of daily use
Benchmarks I verified
- Zero server-side visibility into plaintext data
- No duplicate or missing recurring task instances
- A correct “today” boundary regardless of timezone
- Deleting a recurring task removes the full series
Research & discovery
Learning where mainstream to-do apps lose trust
No primary user research was conducted — this started as a personal tool, and I’m upfront about that. What I did do was an informal competitive review: checking how Todoist, TickTick, and Lunatask actually describe their security posture, not just assuming. The takeaway was consistent: nearly every mainstream to-do app treats security as a server-side guarantee — encrypted at rest — not a promise the provider itself can’t read your data. Lunatask is the one real exception, but it asks you to adopt an entire life-tracking system to get there.
Methods
- Competitive review
- Security-posture check
- Dogfooding as usability testing
- Architecture review
- Bug pattern analysis
- Real daily use
User personas
One validated user, two informed hypotheses
Since this is a solo, personal-use project, only one persona is backed by real, validated use. The other two are informed hypotheses based on the market and the app’s feature set — not confirmed through interviews.
JValidated
Jewell
Primary user
A privacy-conscious professional who mixes hard scheduling with personal notes and doesn’t want that content sitting in plaintext on a third-party server.
FHypothetical
The Freelancer
Knowledge worker
Handles client details or financial notes alongside regular tasks; doesn’t fully trust mainstream SaaS to-do apps with that content.
PHypothetical
The Planner-Journaler
Habitual note-taker
Blends task tracking with informal daily notes; wants a fast “just capture it” entry point instead of a rigid task form.
User flow
From loose thought to structured task
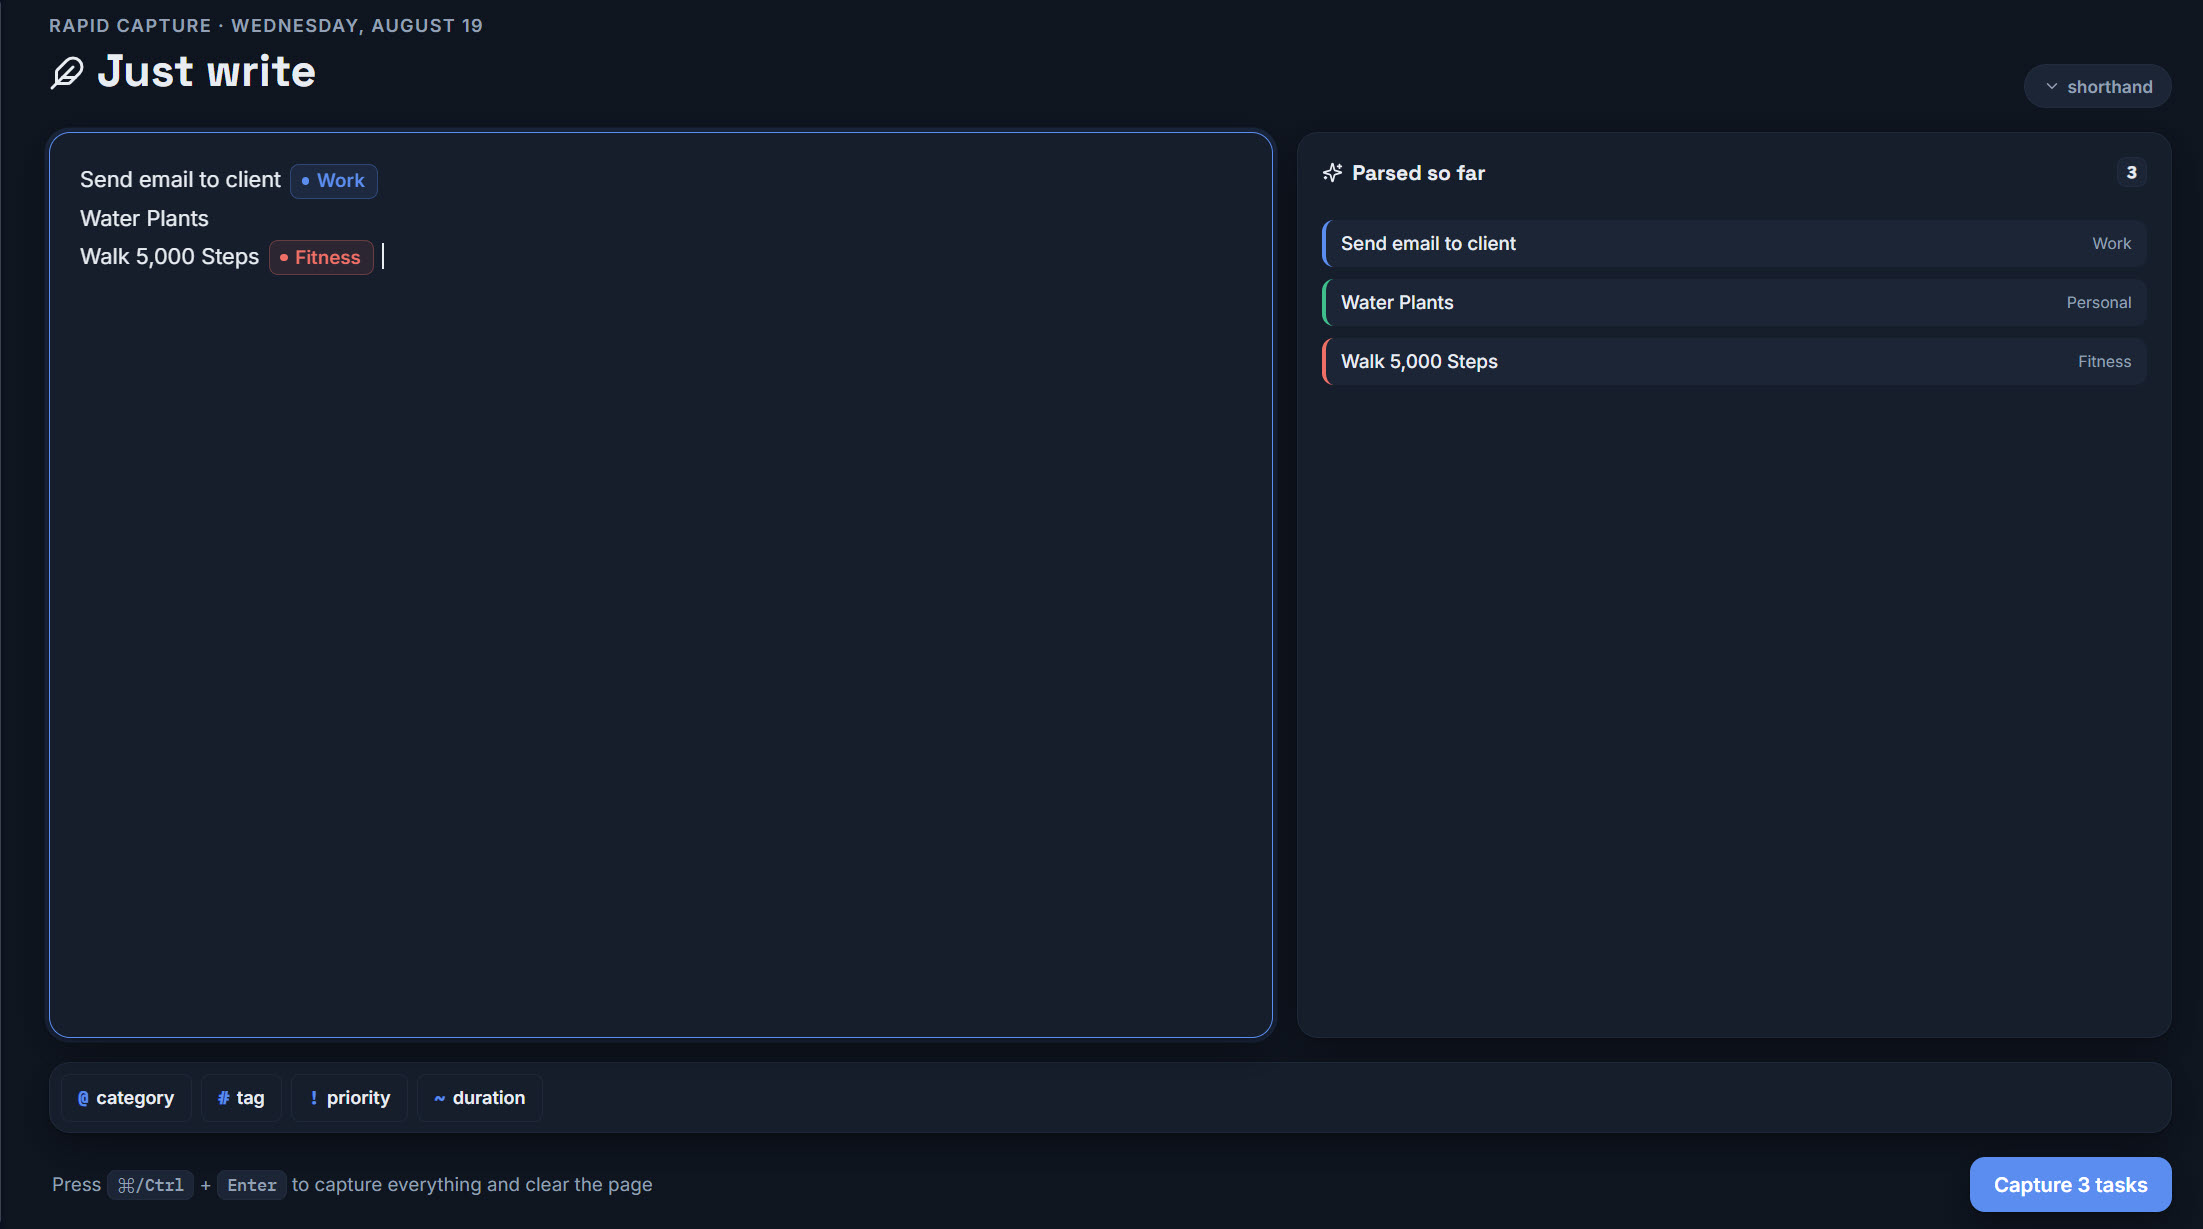
The core flow — quick capture — was designed to remove friction at the exact moment someone thinks of a task.
01
Capture
Types loose text the moment a task comes to mind — no form, no dropdown.
02
Parse
@category and #tag shorthand gets parsed into a structured task automatically.
03
Organize
The task lands in the right category card on Today, ready to act on.
04
Protect
Everything is encrypted client-side before it’s ever sent anywhere.
Information architecture
Time horizon first, category second
Navigation is organized around time horizon — Today for the immediate view, Monthly for the broader one — with categories as the organizing layer inside each: Login, Today, Monthly/Calendar, Quick Capture, and Settings.
- Login
- Today
- Monthly / Calendar
- Quick Capture
- Settings
Encrypted at rest isn’t the guarantee privacy-conscious users actually want.
UI design
Hand-built, and quiet enough to get out of the way
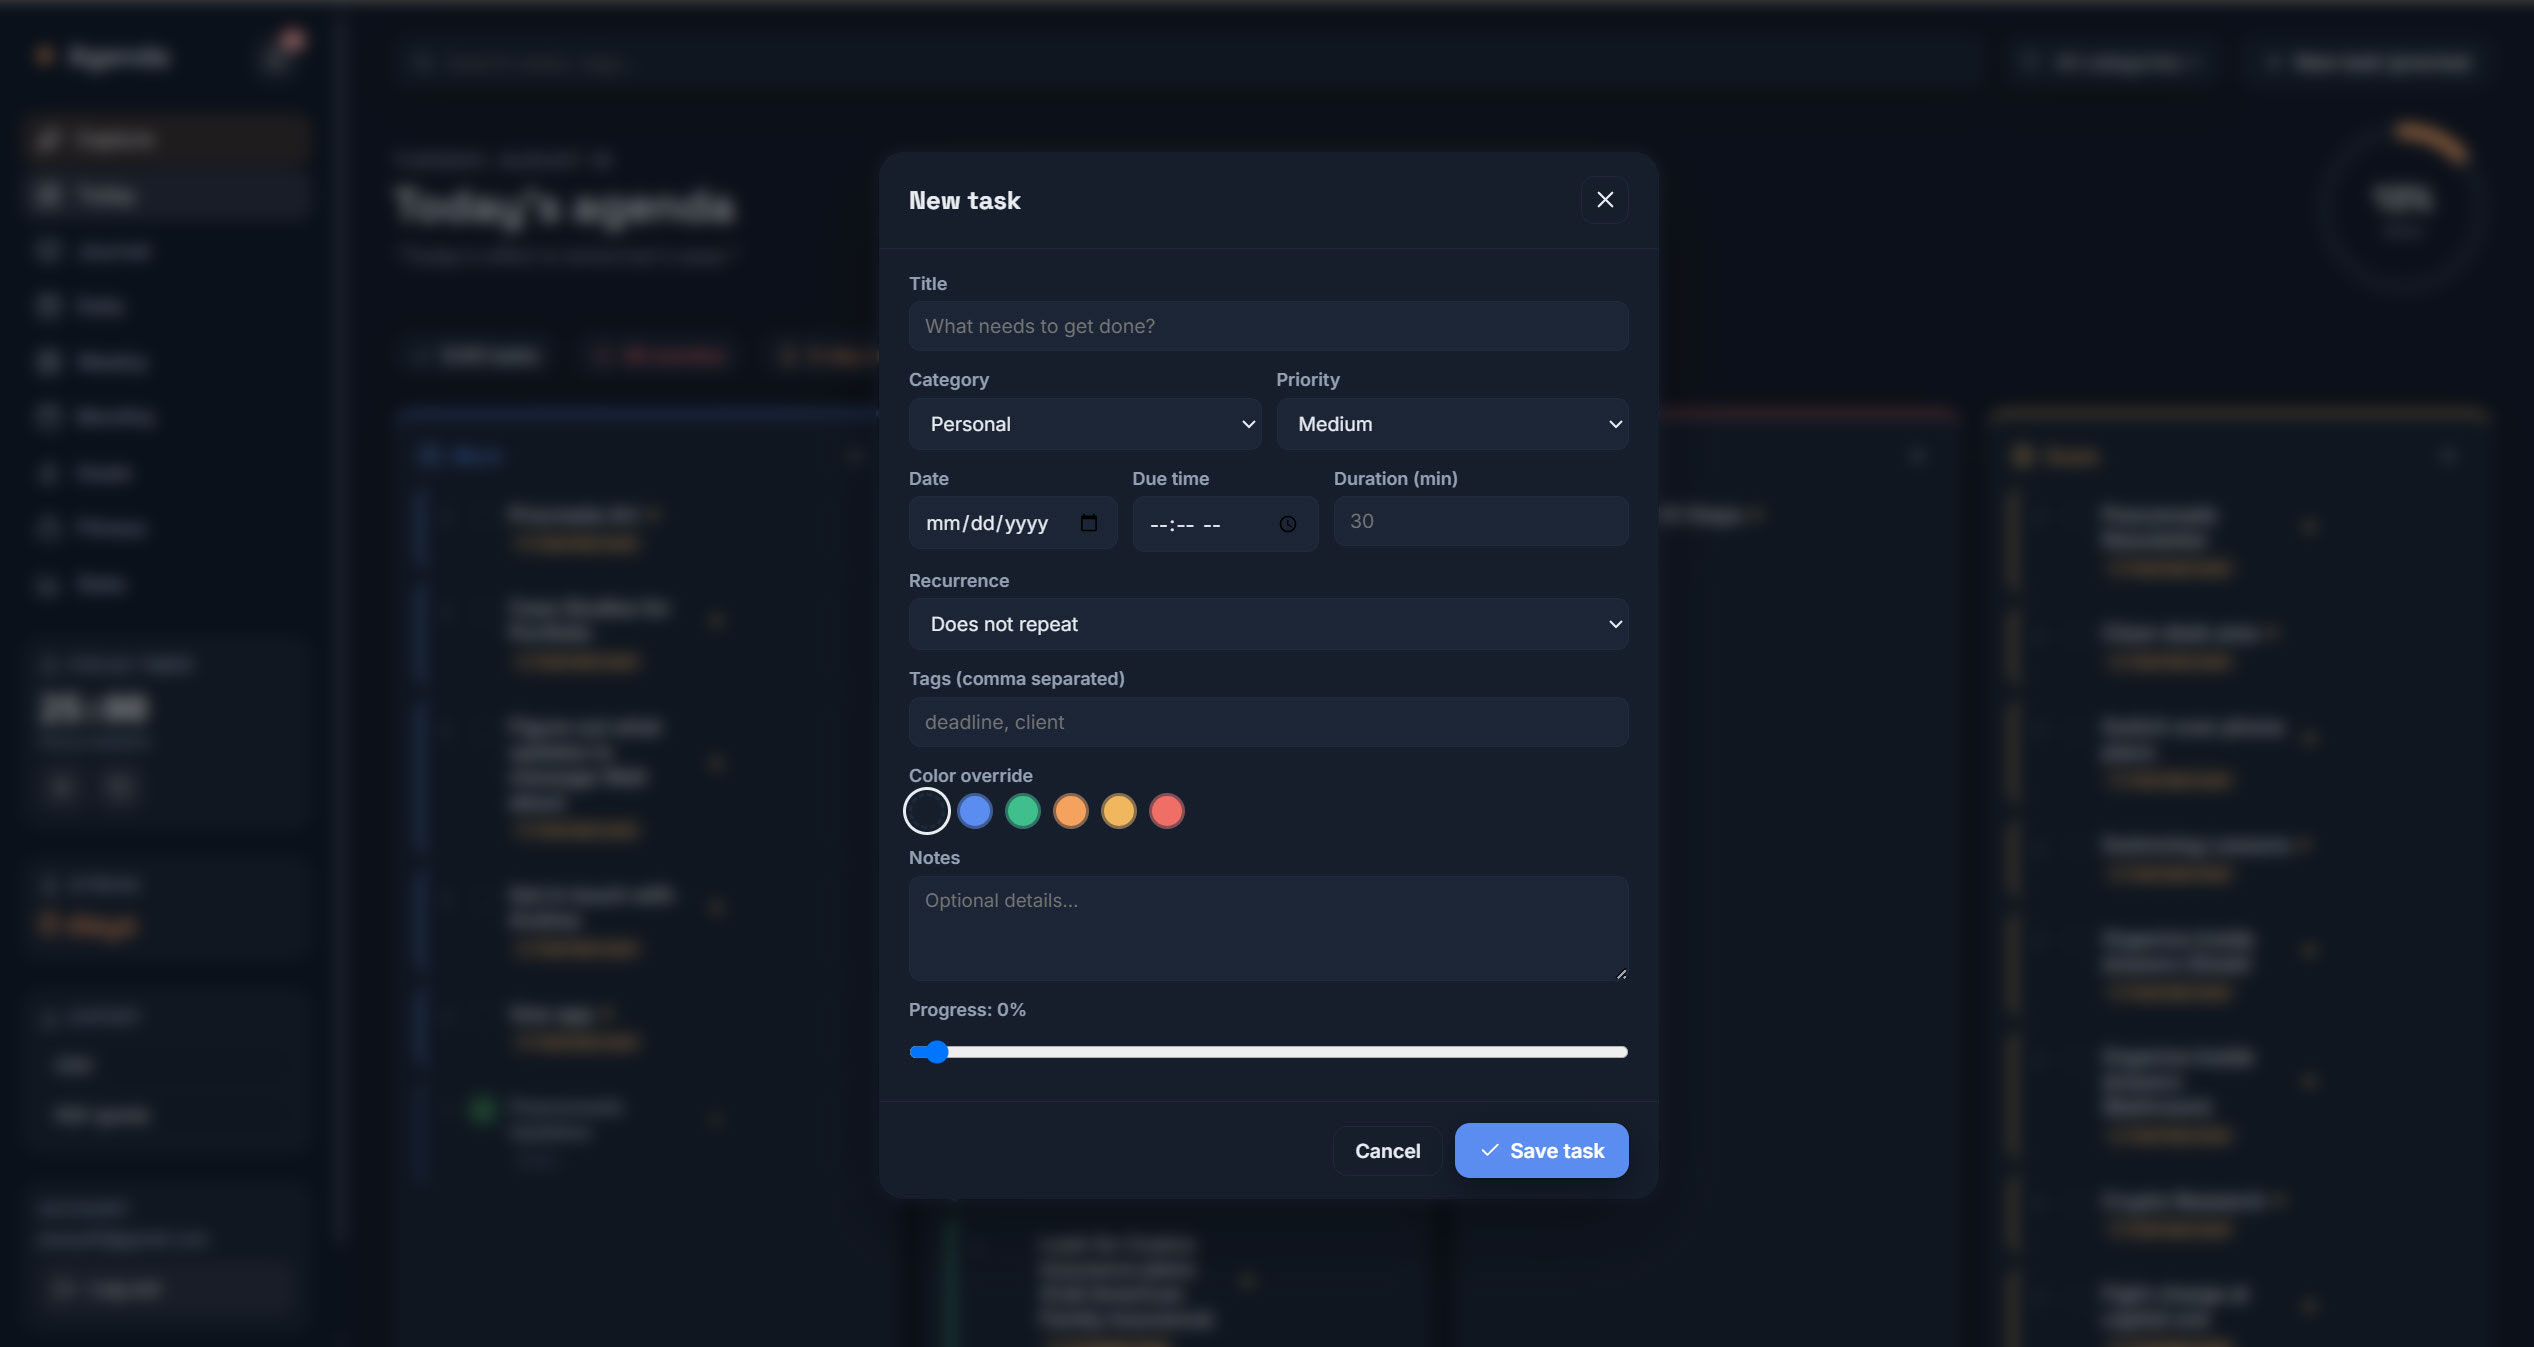
The UI is a hand-built design system — no CSS framework — with light and dark themes both driven off CSS variables. Building every component by hand kept visual choices tied to how the app should feel to use daily, not to what a component library defaults to.
Final solution
A planner that does the whole job
The shipped app pairs a Today view organized into category cards with a Monthly calendar, non-destructive task carryover, recurring tasks that generate and delete correctly, drag-and-drop reorganization, and a fast quick-capture flow — all wrapped in a hand-built light/dark UI.
Underneath, genuine client-side end-to-end encryption (AES-256-GCM + PBKDF2) means none of it is readable without my passphrase. Changes go to a preview first, so nothing ships until I’ve checked it.
Accessibility
Where it stands today
Accessibility hasn’t had a formal audit yet, and I want to be direct about that rather than overstate it. A few things are already in place by design — light/dark themes for different lighting and visual comfort, standard semantic form elements, and proper autocomplete attributes so password managers can fill the passphrase field.
Recommended next — not yet done
- Keyboard navigation audit
- Color contrast check (light + dark)
- Screen reader pass
- Focus state review
Results & impact
From personal frustration to a tool I actually trust
Genuine privacy
Zero server-side visibility into task data, enforced architecturally, not promised in a policy.
Reliable mechanics
Recurring tasks, carryover, and categorization behave correctly under real daily use.
Actually used, daily
The clearest proof point — it replaced the apps I didn’t fully trust, and I still use it every day.
There’s no adoption or engagement data to report — it’s a private tool with no analytics, by design. The impact is that every bug in this case study was found and fixed through real use, not a test environment, and it’s still the planner I open every day.
Skills demonstrated
What this project shows
- Product strategy
- Information architecture
- Hand-built design systems
- Front-end engineering (React)
- Full-stack development
- Applied security architecture
- Debugging & QA
- Technical UX writing
- Solo end-to-end delivery

Next case study
Peacemade Craft: an art shop built on trust.
A WordPress and WooCommerce store for original artwork and commissions, designed so first-time visitors feel safe buying.
Like what you see?
I turn complex problems into products that actually work — end to end. Let’s talk about yours.